
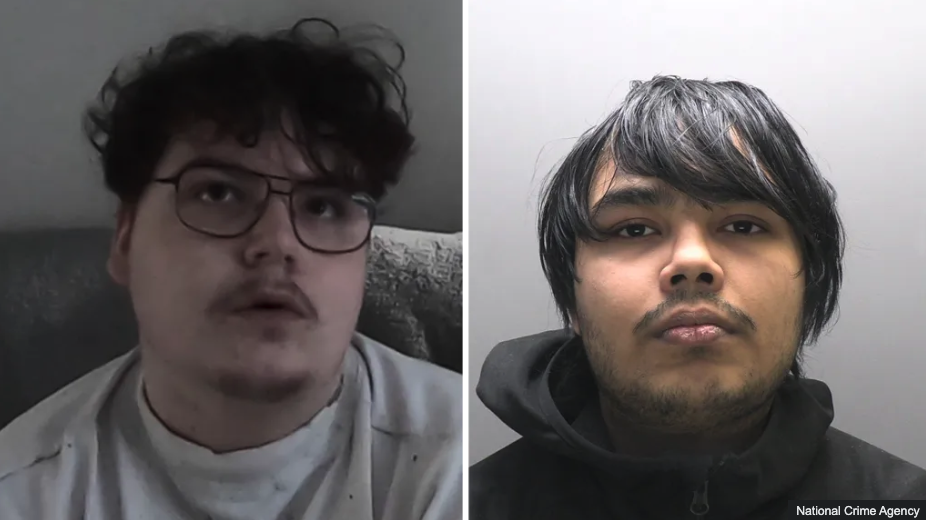
When a six-week criminal trial was scheduled to begin in a London courtroom this week, prosecutors likely anticipated an arduous legal battle. Instead, two defendants associated with one of the most consequential cybercrime organizations in recent memory entered guilty pleas before proceedings could properly begin — a development that underscores both the strength of the evidence assembled against them and the accelerating pace of international enforcement action targeting the group known as Scattered Spider.
Who Are the Defendants?
Thalha Jubair, 20, of East London, and Owen Flowers, 18, of Walsall, admitted to conspiring to carry out unauthorized intrusions against Transport for London's computer infrastructure in August 2024. That attack paralyzed a critical pillar of Greater London's public transport network, disrupting services relied upon by millions of daily commuters and causing cascading operational failures across the system.
Flowers separately admitted involvement in a conspiracy targeting two major US-based healthcare organizations — SSM Health Care Corporation and Sutter Health — in September 2024, raising the stakes of his criminal exposure considerably. For Jubair, the legal jeopardy extends even further: US federal prosecutors in New Jersey have unsealed an indictment connecting him to over 120 network intrusions affecting 47 American entities between May 2022 and September 2025, with victims collectively paying an estimated $115 million in ransom payments.
A Criminal Résumé That Stretches Back Years
The scale and sophistication of the activity attributed to these individuals is remarkable — particularly given their ages. Jubair allegedly co-administered a Telegram channel called Star Chat, which operated as a commercial hub for SIM-swapping services. The group gained unauthorized access to internal systems at major wireless carriers in both the US and UK, then monetized that access by offering a subscription-style service: redirect a target's phone number to attacker-controlled hardware, intercept calls and SMS messages, and effectively neutralize any multi-factor authentication protecting the victim's accounts.
The industrialization of SIM-swapping — turning a sophisticated attack into a purchasable service — represents a significant evolution in the cybercriminal economy, and one that defenders have been slow to adequately counter.
Jubair's alleged criminal activity predates even these operations. Investigators have linked him — at age 15 — to the sale of fraudulent emergency data requests, wherein compromised law enforcement and government email accounts were used to demand sensitive subscriber information from major technology platforms. By fabricating the appearance of urgent legal authority, these requests bypassed normal judicial oversight entirely.
Flowers, meanwhile, is believed to be the individual who gave anonymous media interviews following Scattered Spider's audacious September 2023 ransomware attacks on Las Vegas casino operators MGM Resorts and Caesars Entertainment — attacks that caused hundreds of millions of dollars in combined losses and drew intense public attention to the group's capabilities.
The Broader Scattered Spider Enforcement Picture
The guilty pleas from Jubair and Flowers are the latest developments in what has become a sustained, multi-jurisdictional effort to dismantle Scattered Spider's membership. The group has been linked to intrusions at Marks & Spencer, Harrods, and the Co-op Group in the UK, as well as an extraordinarily prolific SMS phishing campaign in the summer of 2022 that compromised single sign-on credentials across more than 130 organizations — among them LastPass, DoorDash, Mailchimp, Plex, and Signal.
The legal accountability has been building steadily:
Jubair and Flowers are scheduled to be sentenced in London on July 15, 2026. Jubair also remains a wanted individual in the United States, suggesting his legal exposure may extend well beyond the current UK proceedings.
What This Reveals About Modern Cybercrime
Scattered Spider's operational model illustrates several uncomfortable truths about the current threat landscape. The group demonstrated that teenagers with social engineering skills and access to criminal service markets can outmaneuver the security programs of Fortune 500 companies and government-adjacent infrastructure alike. Their preferred techniques — voice phishing, SMS lures, SIM-swapping, and credential theft — require relatively little technical sophistication but consistently achieve devastating results against organizations that have not adequately hardened their human attack surface.
The group also operated with a brazenness that was, until recently, largely consequence-free. Giving media interviews after a major ransomware attack, running public Telegram channels offering criminal services, and compromising healthcare providers with apparent impunity — these are not the hallmarks of an operation that feared law enforcement intervention. The current wave of prosecutions signals that this calculation has shifted.
What You Should Do
The Scattered Spider cases carry direct operational lessons for security teams and organizational leadership:
- Treat telephony as a threat vector. SIM-swapping attacks succeed because organizations rely on SMS-based authentication as a security control. Migrate to hardware security keys or authenticator app-based MFA wherever possible, and eliminate SMS as an account recovery option for privileged access.
- Invest in voice phishing (vishing) awareness training. Many of Scattered Spider's intrusions began with a phone call, not a malicious link. Help desk staff and IT personnel must be trained to verify identity through out-of-band, pre-established mechanisms — not caller-provided information.
- Monitor for emergency data request abuse. Technology platforms should implement enhanced verification protocols for any legal process arriving via email, particularly requests framed around urgency or imminent harm.
- Assume credential compromise at scale. The 2022 SMS phishing campaign affected over 130 organizations simultaneously. Threat intelligence sharing and rapid credential invalidation processes are essential for limiting blast radius when campaigns of this scope emerge.
- Review telecom provider access controls. Wireless carriers with internal tools accessible to employees represent a significant supply chain risk. Organizations should pressure carriers on their own internal access controls as part of vendor security assessments.
The Scattered Spider prosecutions are a meaningful enforcement milestone, but the underlying attack techniques that made the group so effective remain fully operational in the hands of other threat actors. The courtroom victories are important — but they are not a substitute for closing the structural vulnerabilities that allowed a group of teenagers to extort hundreds of millions of dollars from some of the world's largest organizations.


