
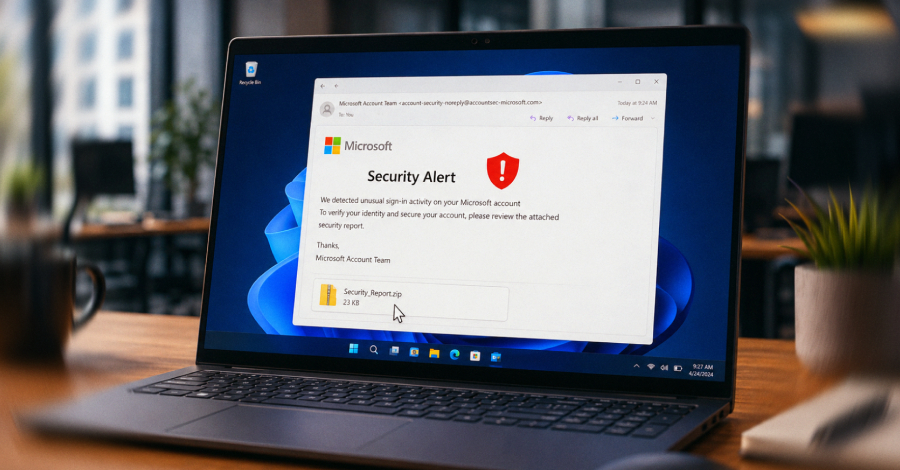
State-sponsored cyber operations out of Pyongyang have long demonstrated a willingness to evolve their tradecraft, and the latest campaign attributed to the North Korean threat actor known as ScarCruft — also tracked as APT37 — is a sharp reminder of how effectively social engineering can serve as the entry point for advanced intrusions. The group has been observed leveraging spear-phishing emails meticulously crafted to resemble official Microsoft Account security notifications, using that manufactured urgency to deploy a previously documented remote access trojan (RAT) called NarwhalRAT.
The Anatomy of a Deceptive Campaign
What makes this campaign particularly dangerous is its exploitation of institutional trust. Microsoft security alerts are a routine part of modern digital life — users receive them when signing in from new devices, when suspicious activity is detected, or when account credentials may be at risk. ScarCruft has weaponized that familiarity with clinical precision.
The phishing messages are engineered to provoke anxiety. Recipients are led to believe their Microsoft account has been accessed without authorization, creating psychological pressure to act quickly — and carelessly. That emotional manipulation is a hallmark of effective social engineering: bypass rational evaluation by triggering an instinctive response.
"Urgency is the adversary's greatest ally. When a user believes their account is under immediate threat, their instinct to act overrides their instinct to verify."
Once a target interacts with the malicious content embedded in the email — whether through a link, an attachment, or a macro-laden document — NarwhalRAT is silently deployed onto the victim's system, establishing a foothold for deeper network compromise.
NarwhalRAT: Capabilities and Threat Profile
NarwhalRAT is a full-featured remote access trojan designed to give its operators persistent, covert control over infected endpoints. While specific technical capabilities can vary across versions and deployments, RATs of this class typically offer:
For a nation-state actor like ScarCruft, whose primary mandate includes espionage operations against South Korean government entities, journalists, defectors, and geopolitical targets, NarwhalRAT represents an ideal instrument for long-term, low-noise surveillance.
ScarCruft's Expanding Playbook
APT37 has been active for well over a decade and maintains a reputation for consistent innovation in its delivery mechanisms. The group has previously leveraged zero-day vulnerabilities, malicious Android applications, and Hangul Word Processor exploits — a software package common in South Korea — to reach its targets. The pivot toward Microsoft impersonation reflects an adaptive strategy: as organizations harden their technical defenses, adversaries increasingly invest in the human attack surface.
This campaign also underscores a broader trend across nation-state threat groups: the convergence of technically sophisticated malware with low-cost, high-yield social engineering. Developing a convincing phishing email requires far fewer resources than discovering a zero-day exploit, yet the operational return can be equivalent when targeting individuals who lack security awareness training.
Why This Threat Demands Organizational Attention
Security teams should resist the temptation to classify this as a geopolitically contained threat relevant only to Korean peninsula targets. ScarCruft has demonstrated interest in defense contractors, think tanks, media organizations, and governmental bodies across Europe, the Middle East, and North America. Any organization operating in sectors of interest to the North Korean regime — energy, defense, diplomacy, technology — should treat this campaign as directly relevant to their threat model.
Furthermore, the use of a trusted brand like Microsoft as a lure means that even security-conscious employees can be deceived. Legitimate Microsoft alerts and malicious imitations can be visually indistinguishable to the untrained eye.
What You Should Do
- Train employees to verify account alerts directly. Any security notification claiming urgency should be evaluated by navigating independently to account.microsoft.com — never by clicking embedded links in emails.
- Deploy advanced email filtering with impersonation detection. Modern secure email gateways can flag messages that spoof trusted brands even when they pass basic SPF/DKIM checks.
- Enable multi-factor authentication (MFA) across all accounts. Even if credentials are harvested via a phishing campaign, MFA significantly raises the cost of account compromise.
- Monitor for NarwhalRAT indicators of compromise (IoCs). Work with your threat intelligence provider to ensure relevant IoCs are ingested into your SIEM and EDR platforms.
- Conduct tabletop exercises simulating spear-phishing scenarios. High-value employees — executives, IT administrators, finance personnel — should receive targeted awareness training specific to nation-state-style lures.
- Review and harden endpoint detection rules. Ensure your EDR solution is tuned to detect RAT-associated behaviors such as unusual outbound connections, privilege escalation, and registry persistence modifications.
ScarCruft's latest campaign is not a novel threat — it is a refined one. The combination of a credible brand impersonation, a psychologically manipulative message, and a capable RAT payload represents exactly the kind of layered attack that catches organizations off guard. Awareness, verification habits, and layered technical controls remain the most reliable countermeasures available.


