As reported by SecurityAffairs, U.S. Coast Guard and FBI personnel boarded two Texas-bound energy tankers last month — including the 1,093-foot VL Prosperity carrying approximately 2.3 million barrels of crude — after cyberattacks struck the vessels while underway. Iranian state media claimed threat actors accessed propulsion, navigation, and cargo systems, knocking out communications for roughly 30 hours. While attribution remains under investigation, the incident signals that maritime cyber risk has moved from theoretical concern to active operational disruption.
Why This Matters Beyond the Headlines
The VL Prosperity incident is not an isolated breach — it's a symptom of systemic underinvestment in shipboard OT (operational technology) security. Modern tankers are floating industrial control systems. Integrated bridge systems, engine monitoring, ballast control, and cargo management increasingly run on networked Windows and Linux hosts that share infrastructure with crew email, satellite internet, and third-party maintenance VPNs. The air gap that many operators assume separates safety-critical systems from attack surface largely doesn't exist on vessels built or refitted in the last decade.
Rear Adm. Amy Grable's observation that highly connected vessels are 'susceptible to cyber threats' undersells the urgency. A compromised supertanker isn't just a data breach — it's a potential environmental catastrophe, a navigational hazard blocking a major waterway, or a kinetic event in a congested port. The Lloyd's of London modeled a single major tanker incident in the Strait of Hormuz at $20+ billion in insured losses. Cyber-enablement of that scenario is now demonstrably real.
What Defenders Should Actually Worry About
Who Is at Risk
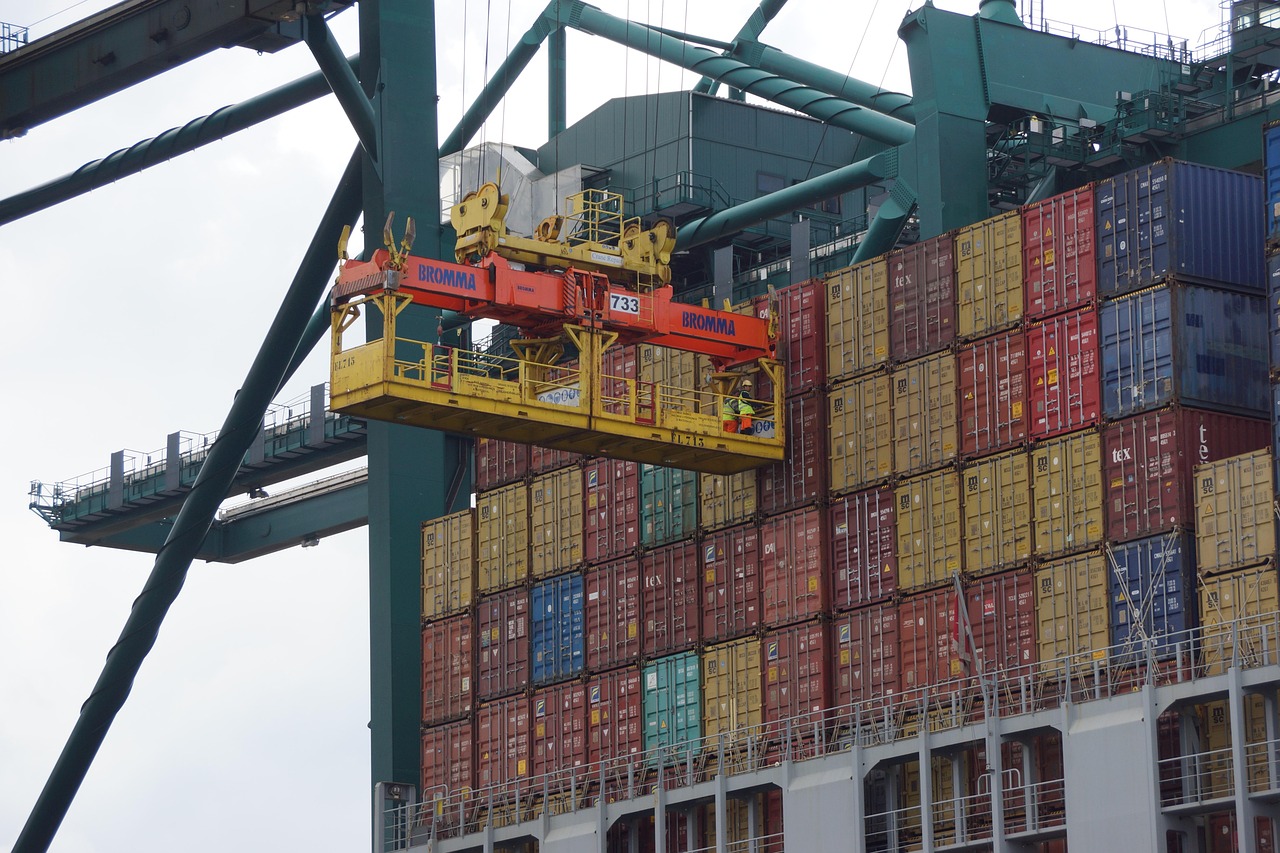
This isn't just a tanker problem. The exposure surface extends to container ships, LNG carriers, offshore platforms, and port terminal SCADA. Any vessel operator using always-on VSAT or hybrid satellite-cellular links without proper segmentation is effectively running a floating unmanaged OT network. The Coast Guard's Cyber Protection Team has conducted 40–50 boardings in the past year — a cadence suggesting this is a pattern, not an anomaly.
Affected stakeholders include: shipowners and operators (ISPS Code compliance exposure), flag states (Liberia, Marshall Islands, Panama), port authorities and terminal operators, classification societies verifying cyber compliance, marine insurers facing silent cyber accumulation, and energy companies whose charter agreements may not adequately allocate cyber risk.
Shield53 Recommendations
Maritime cyber risk management cannot be a compliance checkbox exercise. The IMO's MSC.428(98) resolution has been mandatory since January 2021, yet adoption remains inconsistent across the global fleet. Operators that haven't conducted a genuine OT-focused risk assessment are operating on borrowed time.
Immediate Actions
- Conduct shipboard network architecture review on all vessels — map IT/OT dependencies, identify flat networks, document any hard connections between crew-facing systems and safety-critical controls
- Implement strict network segmentation between bridge, engine room, cargo, and crew networks using VLAN isolation or physical firewalls — no exceptions for 'convenience'
- Deploy OT-aware monitoring on vessel networks — passive network sensors that detect anomalous lateral movement without disrupting ship systems
- Harden remote access — enforce MFA on all satellite and shore-side VPN connections, implement jump hosts for third-party access, maintain access logs for minimum 90 days
- Establish vessel cyber incident response plans that account for loss of navigation, communications, or propulsion — including manual override procedures and shore-side escalation contacts
Strategic Priorities
- Integrate cyber risk into existing Safety Management Systems (SMS) per ISM Code — treat cyber as a safety hazard, not just an IT problem
- Engage classification societies for Cyber Managed (CybR) notation on high-value vessels
- Pressure VSAT providers for network-level security controls, not just bandwidth
- Develop fleet-wide vulnerability management for shipboard OT, including patching cadence and EOL system replacement plans
The maritime sector has historically treated cybersecurity as a shoreside concern. The VL Prosperity incident makes clear that the attack surface is now 1,000 feet long, floating, and carrying two million barrels of crude. The next major maritime cyber incident won't be a warning — it'll be a spill.