
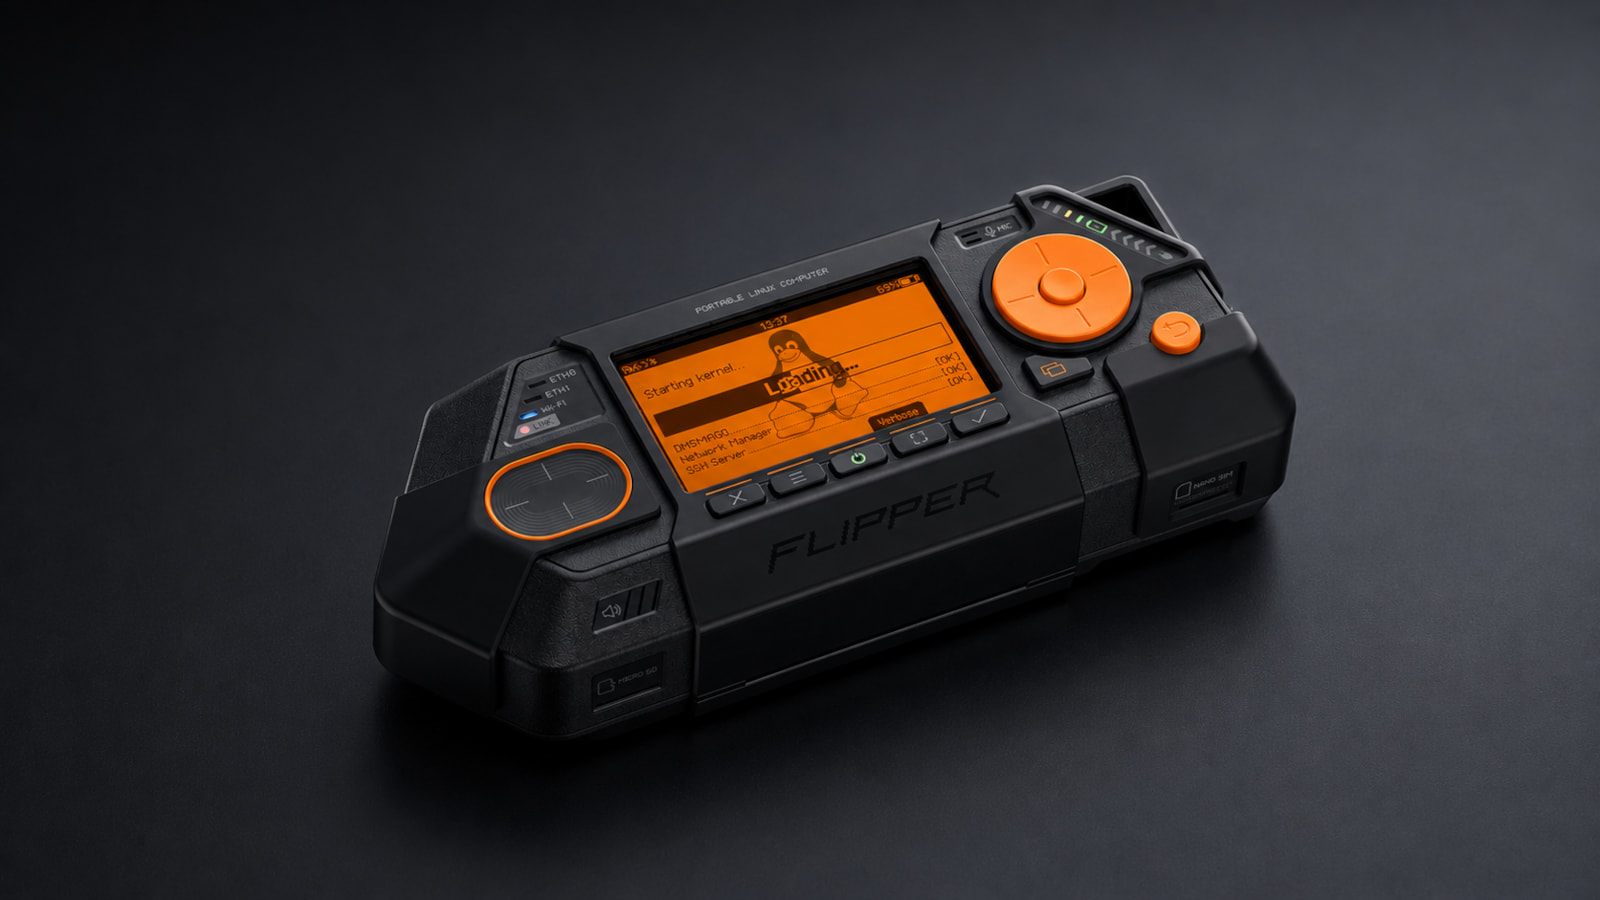
The cybersecurity community is witnessing an unprecedented attempt to democratize penetration testing hardware through the ambitious Flipper One project. This initiative represents more than just another gadget launch—it's a stark illustration of the systemic challenges plaguing modern ARM-based hardware development and the critical gaps in open-source infrastructure that security professionals depend on.
The project's technical specifications reveal significant ambitions: a Rockchip RK3576 ARM system-on-chip paired with 8GB RAM, complemented by a Raspberry Pi RP2350 microcontroller in an innovative dual-processor configuration. This architecture enables the device to maintain operational capability even when the primary Linux system is powered down—a feature particularly valuable for field security assessments where reliability is paramount.
Modular Design Meets Security Requirements
The modular approach represents a significant departure from traditional penetration testing tools. With support for M.2 and GPIO interfaces, plus connectivity options including PCIe, USB 3.1, SATA, and satellite communication capabilities, the platform positions itself as a comprehensive security research workstation. The ability to integrate software-defined radio equipment, AI accelerators, and 5G modems creates unprecedented possibilities for advanced threat simulation and network analysis.
However, the project's current development challenges expose deeper issues within the ARM ecosystem that affect the entire cybersecurity industry. The team's struggle with proprietary components and vendor dependencies highlights a critical vulnerability in our security infrastructure: the reliance on closed-source firmware and drivers that cannot be independently verified or modified.
The ARM Linux Crisis
Perhaps most concerning is the project's candid assessment of the ARM Linux landscape. The development team describes the current state as "depressing," citing widespread use of closed boot components, vendor-specific modifications, and incomprehensible board support packages. This fragmentation creates significant security implications, as it becomes virtually impossible to conduct thorough security audits of the underlying platform.
The reliance on proprietary components creates an inherent trust boundary that security professionals cannot cross, potentially compromising the integrity of security assessments conducted on these platforms.
The collaboration with Collabora to achieve mainline Linux kernel support for the RK3576 represents more than just a technical milestone—it's an essential step toward creating auditable, trustworthy security tools. Without this foundation, the cybersecurity community remains dependent on black-box solutions that may contain unknown vulnerabilities or backdoors.
Economic and Technical Realities
The project's transparency about its challenges provides valuable insights into the economics of hardware security tool development. The team acknowledges significant financial risks, including supply chain disruptions affecting critical components like RAM chips. These economic pressures often force compromises in security features or force reliance on proprietary solutions that undermine the open-source principles essential for trustworthy security tools.
The technical hurdles—ranging from USB-C DisplayPort implementation to hardware-accelerated video encoding—demonstrate the complexity of modern hardware integration. Each of these challenges represents potential attack vectors that must be carefully evaluated in any security assessment platform.
Community-Driven Development Model
The open call for community participation represents both an opportunity and a risk for the cybersecurity industry. While crowdsourced development can accelerate innovation and improve security through transparency, it also requires careful coordination to ensure security best practices are maintained throughout the development process.
The project's modular software architecture, including the FlipCTL framework and custom user interface for small-screen Linux environments, could establish new standards for portable security workstations. However, the success of these innovations depends heavily on the security community's willingness to contribute expertise and resources.
Key Takeaways for Security Professionals
The Flipper One project serves as a microcosm of broader challenges facing cybersecurity tool development. Its ultimate success or failure will provide crucial insights into the viability of community-driven approaches to creating trustworthy security infrastructure. For security professionals, this project represents an opportunity to shape the future of penetration testing tools while addressing fundamental issues in hardware trustworthiness and supply chain security.


