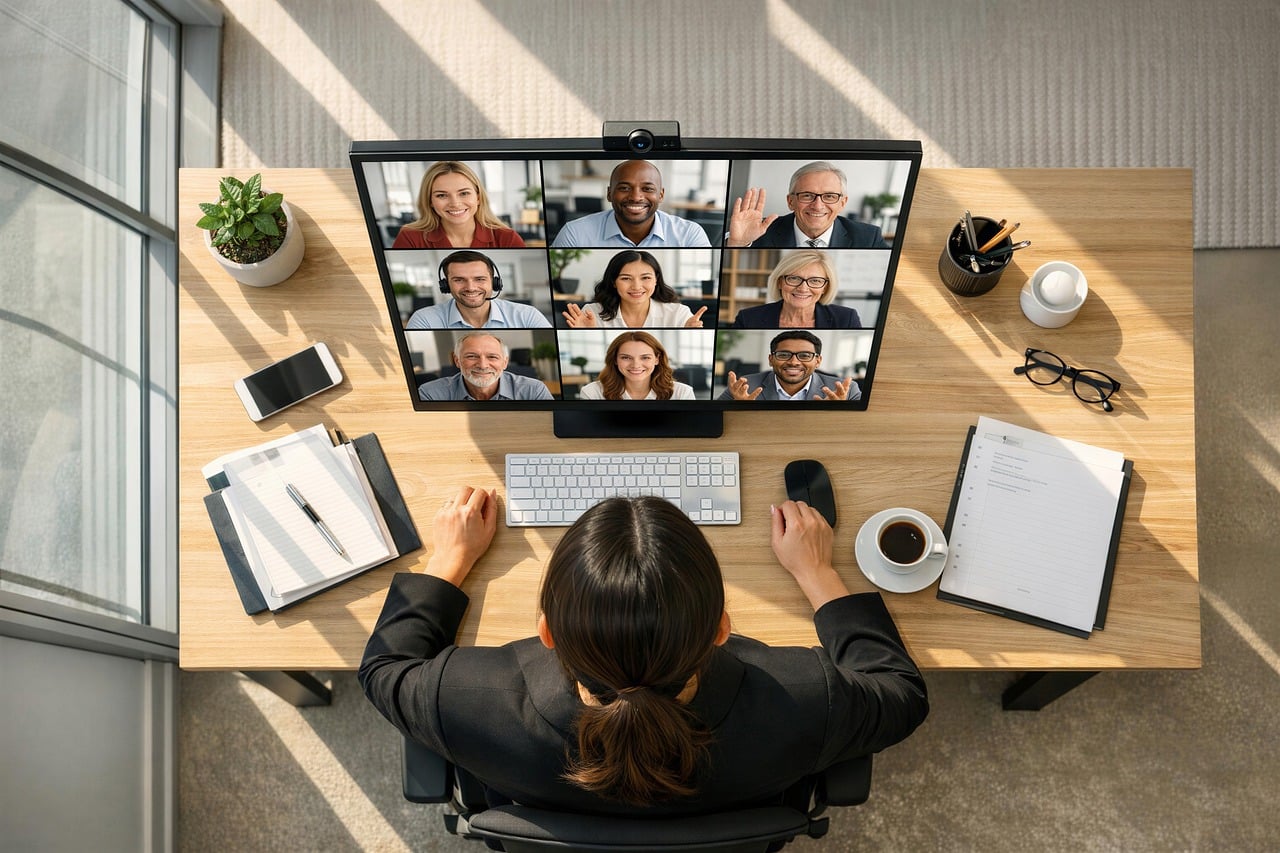
As reported by The Hacker News, the FBI has attributed a sprawling $400 million cryptocurrency theft campaign to North Korean state-linked actors using a social engineering scheme codenamed FaceStealer. The campaign, active over the last 18 months and tied to the BlueNoroff threat cluster (also tracked as APT38, Sapphire Sleet, and CryptoCore), weaponizes deepfake video calls and ClickFix-style malware delivery to compromise individuals across the cryptocurrency and Web3 sectors. This is a watershed moment for social engineering — not because the tactics are novel, but because the scale, AI-enablement, and convergence of techniques represent a mature, industrialized deception pipeline.
Why This Matters
The FaceStealer campaign demonstrates that North Korean operators have fully integrated generative AI into their social engineering workflows. The use of what the DOJ calls "super intelligence (SI)" to create deepfakes of known cryptocurrency industry figures is not a theoretical future threat — it is operational now and has been for over a year. The attack chain is particularly insidious because it abuses the inherent trust mechanics of video communication: seeing a familiar face and hearing a familiar voice in real-time.
The attack doesn't exploit a software vulnerability — it exploits human trust, amplified by AI-generated authenticity. No patch can fix that.
The campaign's connection to the broader TraderTraitor activity — which saw the DOJ seize $1.2 billion in stolen cryptocurrency tied to the Binance exchange compromise — signals that DPRK cyber operations are generating revenue at a scale comparable to small nations' GDP. These proceeds directly fund Pyongyang's weapons programs, making every successful compromise a national security concern.
The Attack Chain: More Sophisticated Than It Appears
Shield53 analysis of the FaceStealer methodology reveals a multi-stage deception pipeline that deserves closer examination:
This replay-and-record loop is self-reinforcing: each victim's recorded video becomes ammunition for the next. Kaspersky's October 2025 documentation of the related GhostCall campaign confirms this has been operational for at least a year, meaning the threat actors have had ample time to refine their deepfake quality and social engineering scripts.
Who Is at Risk
The primary targets are individuals in the cryptocurrency, decentralized finance (DeFi), and Web3 sectors — including developers, executives, venture capital partners, and exchange employees. However, the methodology is fully portable. Any organization where high-trust video communication is routine — financial services, legal, M&A advisory, executive recruitment — should consider itself a viable future target. The BlueNoroff cluster has historically pivoted to follow the money, and the success of this campaign virtually guarantees expansion.
Shield53 Recommendations
Defenders must treat video-based social engineering as a primary threat vector, not a niche concern. The following actions should be prioritized immediately:
- Verify out-of-band: Establish a policy where any meeting invitation involving financial discussions, credential sharing, or software installation must be verified through a secondary, pre-established communication channel (phone call to a known number, in-person confirmation)
- Train for deepfake detection: Update security awareness training to specifically address deepfake video calls. Teach employees to watch for micro-artifacts: unnatural blink patterns, lip-sync desynchronization, inconsistent lighting, and refusal to perform spontaneous gestures or turn their head in unexpected ways
- Block ClickFix delivery paths: Deploy application control and browser security policies that prevent execution of downloaded binaries from meeting platforms. Use allow-listing for any legitimate troubleshooting tools and block all others by default
- Isolate meeting environments: Conduct video meetings with external parties from non-production systems or dedicated meeting endpoints that lack access to cryptocurrency wallets, seed phrases, SSH keys, or corporate credentials. Treat every external video call as potentially hostile
- Detect the replay loop: Monitor for signs that employees' video streams may have been recorded — unusual outbound traffic during video calls, unauthorized screen capture tools, or newly installed meeting software on corporate endpoints
- Secure seed phrases and wallet credentials: Enforce hardware-based key storage for all cryptocurrency assets. No software-only wallet should be accessible from any machine that participates in external video calls
- Brief high-value targets individually: Executives, founders, and key developers in the crypto space should receive one-on-one briefings on this specific campaign. General training is insufficient for individuals who are actively being targeted
The FaceStealer campaign is a preview of the next decade of social engineering. As generative AI tools become more accessible, the cost of producing convincing deepfakes will approach zero, while the cost of detecting them will rise. Organizations that fail to build human and technical defenses against AI-amplified deception now will find themselves permanently on the back foot. The $400 million stolen by BlueNoroff in 18 months is likely just the beginning.