
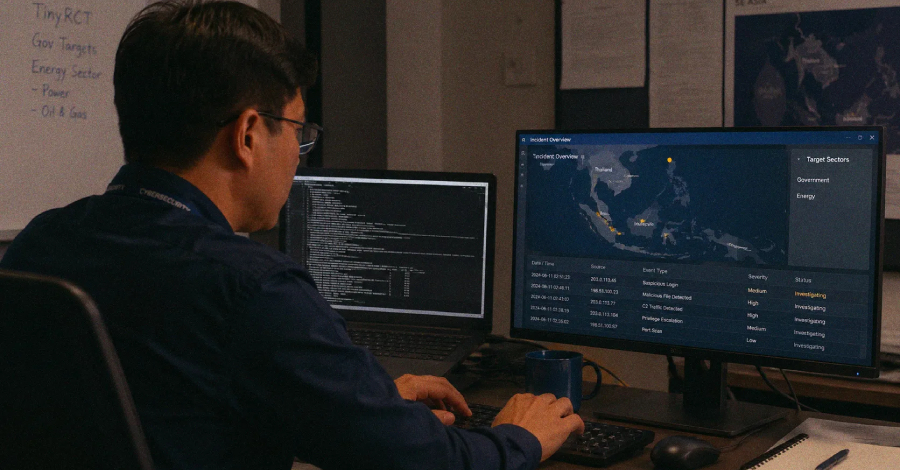
A calculated and methodical cyber espionage campaign is quietly unfolding across Southeast Asia, with state-owned enterprises and government ministries in its crosshairs. Security researchers have identified a previously undocumented threat actor — designated CL-STA-1062 — deploying a custom-built backdoor known as TinyRCT in a series of intrusions targeting the region's energy sector and government institutions. The sophistication of the tooling, combined with the strategic nature of the targets, points unmistakably toward a Chinese-speaking advanced persistent threat (APT) with clearly defined geopolitical objectives.
A New Tool in a Familiar Playbook
TinyRCT represents a significant tactical evolution in the threat landscape targeting Southeast Asian critical infrastructure. While the malware's name suggests a degree of minimalism, its capabilities are anything but trivial. Custom backdoors of this nature are typically reserved for high-priority operations — built specifically to evade detection by standard endpoint security tools that rely on known malware signatures.
What makes TinyRCT particularly concerning is its apparent purpose: establishing persistent, covert remote access within the networks of organizations that underpin national energy supply chains and government communications. This is not opportunistic cybercrime. This is strategic infiltration with long-term intelligence collection as the likely end goal.
"Custom-developed backdoors deployed against critical infrastructure are a hallmark of state-sponsored operations — they signal patience, resources, and a very specific mission brief."
The actor's focus on state-owned enterprises is particularly telling. These organizations sit at the intersection of government policy and national economic infrastructure, making them high-value targets for adversaries seeking to monitor strategic decision-making, steal proprietary energy data, or pre-position within networks for potential future disruption.
Attribution and Regional Context
Attributing cyberattacks is never a precise science, but multiple indicators — including linguistic artifacts in the malware, operational patterns, and targeting preferences — align CL-STA-1062 with the broader ecosystem of Chinese-speaking threat actors that have historically prioritized Southeast Asia as a theater of cyber operations.
This is not an isolated incident. The region has seen intensifying cyber activity in recent years, driven by competing territorial, economic, and political interests. Nations across Southeast Asia — many of which are rich in natural resources and occupy strategically vital maritime corridors — have increasingly found themselves in the sights of sophisticated APT groups.
The energy sector, in particular, represents a prime espionage target. Intelligence gathered from energy infrastructure operators can illuminate a nation's production capacity, trade relationships, and infrastructure vulnerabilities — all of immense value to a state-level adversary planning long-term strategic moves.
Technical Implications for Defenders
From a technical defense standpoint, campaigns like this one present several distinct challenges:
What You Should Do
For organizations operating in critical infrastructure — particularly those in Southeast Asia or with business ties to the region — this campaign should serve as an urgent call to action. The following measures are essential:
- Prioritize behavioral detection: Move beyond signature-based tools toward endpoint detection and response (EDR) solutions that identify anomalous behavior patterns rather than known malware hashes.
- Audit remote access pathways: Backdoors like TinyRCT survive by maintaining covert command-and-control channels. Rigorous network traffic analysis and anomaly detection on outbound communications can surface these connections.
- Enforce least-privilege access: Limit the blast radius of any successful intrusion by ensuring users and service accounts have only the minimum permissions necessary for their roles.
- Conduct regular threat hunting exercises: Don't wait for alerts to find threats — proactively hunt for indicators of compromise associated with APT tooling targeting your sector.
- Segment critical operational technology (OT) networks: Energy infrastructure operators should ensure that IT and OT environments are segregated, limiting an attacker's ability to pivot from corporate systems into operational controls.
- Review and harden third-party access: Assess every vendor and partner with network access privileges. A compromised supplier is often the path of least resistance for sophisticated threat actors.
The Bigger Picture
The emergence of TinyRCT and the CL-STA-1062 actor is a reminder that cyber espionage against critical infrastructure is not a theoretical future risk — it is an ongoing, present-day reality. As geopolitical tensions continue to shape the digital battlefield, organizations that manage essential national services must adopt the mindset of persistent vigilance.
Governments and private sector operators alike must invest in intelligence-sharing frameworks, cross-sector coordination, and the kind of proactive defense posture that can detect and disrupt sophisticated intrusions before they achieve their objectives. The window between initial access and meaningful damage is often narrow — and those who prepare now will be the ones who respond effectively when it matters most.


